I am an administrative agent (행정사 — a licensed specialist who prepares and files administrative documents, permits and applications) with an office in Songdo, Yeonsu-gu, Incheon. Here is an episode I encountered in my work.
The investigator's third question was this: How long do you keep your entry records?
The client could not answer. He had never set a period. And that question had nothing at all to do with what had been reported.
The complaint began with a different story
A phone call came first. The voice was fast, and the first sentence was this: I've been told that a personal-information complaint has been filed against me.
We set an appointment, and he came the following afternoon. A man in his late thirties, running two twenty-four-hour unstaffed study cafés in Yeonsu-gu, Incheon. He worked another job during the day and managed the premises remotely. It was his third year in business, with loan repayments running until the spring of the following year.
The complaint itself was simple. One user claimed that the record of his entry times had been passed to someone else.
There were private circumstances behind it. An acquaintance who had been quarrelling with that user came to the café and asked when a particular person had come and gone, and a part-time employee working a short night shift at the time looked at the screen and gave a rough time range.
The client only learned of this after receiving notice of the complaint. The part-time employee had already left the job.
That is the reported incident, and it does not even account for half of this account.
Because no one is present, an unstaffed store looks unrelated to personal information. In fact the opposite is true. With no one there, everything is replaced by records. Who opened the door and when, which seat was used and for how long, when payment was made — all of it remains. Matters that a staffed store would have let pass with human memory pile up intact in a database at an unstaffed one.
And those records are usually not something the owner designed. They are the default settings that came with the store-management software. It is not unusual for three years to pass without ever once looking at what is stored and how.
That was his case too. When I asked at the first consultation what information he held, the answer was "name and phone number, roughly." In reality it was a great deal more.
He had already responded twice on his own
He had already made two moves.
The first was calling the receiving agency. He explained that an employee had done it and that he had never given such an instruction. The officer told him there was a fact-finding procedure and asked him to prepare materials. That was accurate guidance.
The second was contacting the user directly. The intention was to apologise and clear up the misunderstanding. The call did not end well.
This second move is the point that calls for the most caution in practice. Contacting a party directly in a matter still under way, even in good faith, leaves room for a different reading later. In particular, if even a hint of asking for the complaint to be withdrawn creeps in, that in itself becomes a new problem.
After that call he spent several days not knowing what to do, and then he came to the office.
The sentence he repeated most in that first consultation was, "But the employee did it." The feeling is understandable. Still, responsibility for handling personal information rests with the business that processes it. Even for an act performed by an employee, granting that employee access, failing to train, failing to control — those remain the business's own.
Explaining this structure took thirty minutes. I believe those thirty minutes set the direction of the two months that followed. A case carried forward while holding on to a sense of injustice and a case that accepts the structure and moves toward fixing it end differently.
That is true in practical terms as well. In an investigation, the claim that "an employee did it" is almost never accepted. A submission stating that "the management system was inadequate and has now been corrected in these ways," by contrast, is genuinely reviewed.
I separated the matter into two questions
What I did at the first consultation was to split the question in two.
The first question: how should the reported act itself be viewed?
The second question: separately from that act, how will this business's entire way of handling personal information look during an investigation?
Most clients think only about the first. But an investigation starts with the first and moves to the second. The reported incident is only the key that opens the door, and once the door is open, everything inside is visible.
The Personal Information Protection Act (개인정보 보호법) imposes a number of duties on those who process personal information: collection limited to what the purpose requires, setting retention periods and destroying data once they expire, safety measures, publication of a privacy policy, and supervision of entrusted parties. These duties do not come to life only when there is a leak; they apply continuously in ordinary times.
So alongside responding to the complaint, we began a review of the premises as well. This was the most important judgment in the case.
That judgment carries a cost. Review turns up problems you did not know about, and problems that turn up have to be fixed. Do nothing, and you can go on as though those problems do not exist — at least until today.
So the choice belongs to the client. I laid out the two paths and explained what was most likely to happen on each. Answering only the reported matter and moving on is light for the moment. But if another item surfaces during the investigation, you are then in the position of having known and left it.
He thought for about ten minutes and said he would do the review. With loans outstanding on two premises, that was not an easy decision.
Three things the review turned up
Over three days we mapped how personal information was actually handled at the two premises. Three things came out.
First, no retention period had been set. Entry records and payment-related information had remained intact for three years, from the first day of business. It was not that they had not been deleted; the concept of deletion did not exist. The unstaffed-store management software defaulted to indefinite retention, and he did not know the setting could be changed.
Second, no privacy policy was posted. There was a consent checkbox on the sign-up screen, but no document explaining what was collected, for what purpose, and for how long. Because this was an individual start-up rather than a franchise, no one had told him.
Third, the entrustment relationships had not been organised. A cleaning company and a facilities-management company were sharing an account on the store-management software. It had been done for convenience, and that account could look up user information.
The third was the heaviest. The reported incident was a one-off act by a single employee; this was a structural problem.
The client fell silent at this point. I said this to him: it is fortunate that we found it now. An inspector finding it first, and us finding it first, fixing it, and then explaining — these become entirely different cases.
I will note the review method too. No elaborate tools were used. We logged into the store-management software, opened the menus one by one, and wrote into a table what was stored, who could see it, and how long it stayed. Across the two premises there were nineteen items.
Building that table took half a day. It is not difficult. It is simply that no one does it. Before a problem arises, there is no reason to build it.
One more thing came out. An entry list collected during a promotion in the early days of the business remained as a separate file. Names written on paper had been transferred into a spreadsheet, and the promotion had ended more than two years earlier. Continuing to hold information whose purpose has ended is itself a problem. Files like this are usually sitting in some folder on the desktop, forgotten by their owner as well.
We set an order
Two weeks remained until the materials were due. We divided what could be done in that time from what could not.
What we did in the first week was immediate action. We closed the shared account and set up separate accounts by company. Look-up rights were restricted to the necessary scope. We checked the retention setting in the management software, fixed a period, and established a procedure for destroying records past that period.
We did one thing alongside this: before carrying out any destruction, we recorded the existing state. We made a table of what there was, how much, on what basis, and what was deleted. Deleting material while a matter is under investigation means having to explain that act itself later. Leaving a basis for deletion comes before deleting.
What we did in the second week was documentary work. We drafted a privacy policy matching the actual handling practices and posted it. There is one common mistake here: taking someone else's policy off the internet. A policy that differs from reality is worse than none. It amounts to saying that what is written and what is done are two different things.
So we matched every sentence to actual operations. Collection items limited to what is actually taken, the retention period the one we had just set, the entrusted parties the companies we had just organised.
We decided where to post it as well. A policy has to be where users can find it. At an unstaffed store, people look at both the sign-up and payment screens and the in-store notices. Posting it on only one side is, in practice, the same as it not being visible.
There was also something we ran out of time to do: preparing proper staff training materials. Where part-time employees change frequently, training does not end with a single session. We wrote this part in as a plan only, and produced the actual materials after the case had closed.
Not writing down what you have not done as if you had done it matters. What is written in a submission becomes a subject of verification later. Write that everything was completed within two weeks, and a verification request becomes far more awkward.
What went into the written opinion
The written opinion submitted with the materials had four parts.
First, the facts concerning the reported act. Who did what and when, with the verified scope and the unverified scope written separately. We acknowledged as fact that the part-time employee had looked at the screen and mentioned a time range. We also wrote that no fact of printing or transmitting the record had been verified.
Not denying matters. Contest a verified fact and the credibility of the rest of your statements falls with it.
Second, acknowledgment of shortcomings in the management system. There had been no training, no access control, and therefore a state in which such a thing was possible. We wrote it exactly so.
Third, the improvements already completed. This was the centre of the opinion. Account separation, restricted rights, retention periods set, destruction carried out and recorded, privacy policy posted. Each item carried a completion date and a method of verification.
Fourth, plans going forward. We wrote briefly about quarterly rights reviews and a training procedure for new staff. We did not write at length. Writing down plans you cannot keep is the seed of the next case.
We paid attention to order too. Putting the facts first and the improvements after looks natural, but in practice what the reader most wants to know is the third item: what state is this business in now? So we put a single contents page at the front and made the position of the third item immediately visible there.
A submission should be built in the order it will be read. The writer's order of logic and the reader's order of interest are usually different.
The opinion ran to eight pages, five of them supporting evidence for the third item.
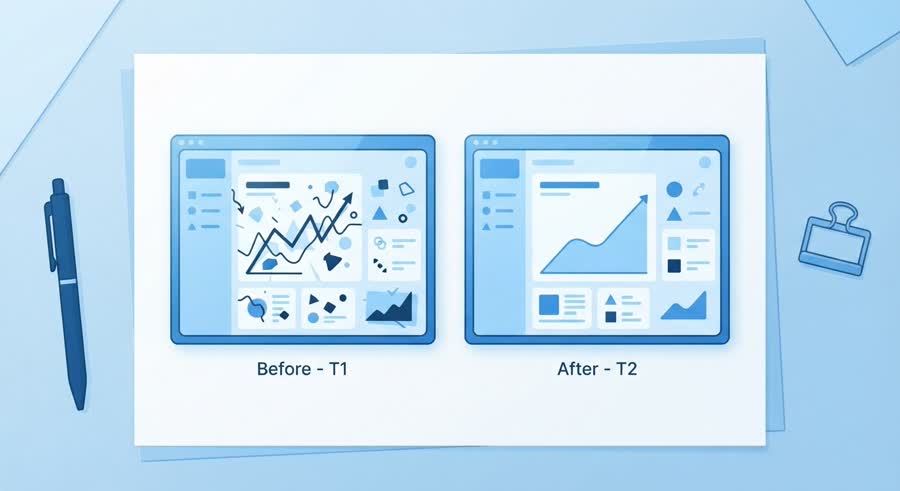
What we watched in preparing the evidence was timing. A screen capture usually carries a date with it. Arrange before and after so they can be compared on the same screen, and the explanatory sentences get shorter. Three paragraphs of writing can be replaced by two images.
There was also something we deliberately did not do: pre-emptively listing and explaining items that had not been raised. It looks like diligence, but in practice it means widening the scope of the investigation yourself. Answer what was asked, show what was fixed, and stop there.
When the follow-up questions came
About three weeks after the materials went in, follow-up questions arrived. There were two.
One was whether the contract with the entrusted companies contained any clause on personal-information handling. It did not. The relationship had been closer to a verbal one. We answered that there was none, and attached a copy of the newly drafted contract with our reply.
The other was the scope of the material that had been destroyed. Seeing this question confirmed again the value of the destruction record we had prepared earlier. What had been deleted, when, and on what basis was all on a single table, so the reply came down to attaching that table and writing two lines of explanation.
Had we deleted without a record, this one question alone would have cost several more weeks. And the credibility of the reply would have been different too.
What helps later in an administrative procedure is usually the record that seemed unnecessary at the time.
That this case was not a "breach notification"
Midway through the consultations the client had one worry. He asked whether the large-scale leak incidents he had seen in the news were the same thing as his case.
Two things needed to be distinguished here.
One is a personal-information infringement complaint. This is the route by which a data subject reports that their own personal information has been handled improperly. This case falls here.
The other is the duty to notify and report a leak. This is the procedure by which a business that learns of a leak of personal information must, where the requirements are met, inform the data subjects and report to the relevant authority. This duty comes with deadlines, and failing to meet requirements that do apply becomes a separate problem in itself.
The two procedures start from different places. In the former the one who reports is the data subject; in the latter it is the business.
Because this case arose from verbally mentioning a particular user's entry times, it was different in character from the type that immediately triggers the notification and reporting duty. Even so, we recorded that judgment briefly in the submission. Writing down the reason for concluding it does not apply is not the same as not mentioning it at all. It means the answer is ready if the point is raised later.
This is also where businesses most often get confused in practice. Requirements and deadlines apply differently from case to case, so where a leak is suspected, it is better to check first rather than put the judgment off.
The line we did not cross
I will also set down clearly what we did not do in this case.
We had no contact with the complainant. There was a request to convey an apology, but I advised that if it were necessary, doing so in writing and within the investigation procedure would be safer. In the end the matter closed without any separate contact.
What we did was to prepare the materials and submissions for the administrative agency, and to bring the premises' handling practices into line with the requirements.
The commotion over two coffees
There was one small commotion in this matter.
On the day the improvements were completed, the client brought two coffees to the office. But he had brought them in tumblers used at the store, and the two looked exactly alike. One had sugar and one did not, and he could not remember which was which either.
In the end both of us took a sip and swapped. That was the longest decision made in the office that day.
He has since set a quarterly review reminder on the store-management screen, I hear. When it appears, running an eye down the list of access rights and moving on takes five minutes.
New part-timers at the second store get a single sheet of A4 on their first day. It says only two things: do not give out user information no matter who asks, and if such a request comes, contact the owner immediately. Make it long and no one reads it, was his explanation.
Rules that last in practice usually look like this. Not perfect, but short — and kept because they are short.
The outcome
The whole period ran about two months. Two weeks from consultation to submission, three weeks for verification and follow-up replies after that, and about three more weeks to close it out.
The outcome was a resolution premised on the improvements. Shortcomings at the premises were noted, and it was confirmed alongside them that measures had already been completed. Specific dispositions vary by case and by individual circumstance, so I do not set them down here.
One point is worth recording, though. The items confirmed at the final stage largely overlapped with the ones we had found and fixed ourselves. In other words, almost nothing new emerged from the investigation. That is why we held on to the second question as well.
Had we not done that review, the same items would have appeared not in our submission but as the other side's findings. The same fact is treated differently depending on who raises it first.
Two things were left to the client in practical terms. One is that the matter is closed. The other is that personal information which had accumulated for three years without any standard now has one.
The second is the larger. The incident first reported was a one-off act by a single employee, and by itself unlikely to recur. A structural problem, left alone, will certainly surface again some day. And it will be heavier then than now.
Being reported ended up becoming the occasion for putting the business in order. I would not recommend this sequence. But once you are already in it, the best that can be done within it is fixed.
I will note the cost as well, since that was his last question. What actually cost money here was the increased software fee from separating accounts, and the time spent redrafting contracts with the entrusted companies. In amount it was not large.
What was genuinely expensive was the three years before it. Records piled up without any standard look as though they cost nothing in themselves, but the moment a problem arises they are billed all at once. And by then the options have narrowed.
In administration, the cheap moment is usually the one when nothing has happened yet.
Two months on, he said something in passing. When he first got the call, he thought this would end with the store closing. It did not turn out that way, but the anxiety of those few days was the kind that cannot be undone.
In administrative procedures it is the time in between, more than the outcome, that wears a person down. Shortening that time is, I think, as substantive a thing as changing the outcome.
A few things to leave behind
If you find yourself in this situation, I would suggest taking things in this order.
① Do not contact the complainant directly. Even contact made in good faith can be read differently while a procedure is under way. If you have something to convey, doing it in writing within the procedure is safer.
② Do not look only at the reported incident. An investigation starts with the complaint and widens to your handling practices as a whole. Reviewing yourself before being told to leads to a different outcome.
③ Check retention periods and access rights first. These are the two most common issues at unstaffed and small premises. Management software often defaults to indefinite retention.
④ Record the current state before deleting anything. The basis and timing of destruction matter more than the destruction itself — especially in a matter still under way.
⑤ Do not copy someone else's privacy policy. A policy that differs from reality can work against you more than having none. Go line by line through collection items, retention periods and entrusted companies against what you are actually doing now.
⑥ Do not share accounts with entrusted companies. Sharing one account for convenience is common, but it leaves a state in which no one can tell who looked up what. Separate accounts by company and limit look-up rights to the necessary scope — that is the baseline.
⑦ Write only what you have actually done. Separating plans from completed work keeps a later verification request from becoming awkward.
Requirements and procedures for personal-information complaints and investigations differ from case to case, and whether the leak notification and reporting duty applies varies with the situation. Individual confirmation is needed.
This case is a fictional account reconstructed to aid understanding; the people, business names, place names and figures in it bear no relation to any specific individual or incident.